Archive
Bruteforce your identity from a single CC number?
In this article and the accompanying white paper, the details that hackers use to take a skimmed or stolen credit card number and work backwards are revealed. They start to figure out your expiry first and then your postal code, CV code and finally your billing address to make purchases as you.
Mastercard holders are winners here because the verification system they use is not vulnerable but visa card holders beware.
Fortunately for card holders, they are indemnified against fraudulent purchases but if you only have one card you may be stuck waiting for a replacement.
https://www.schneier.com/blog/archives/2016/12/guessing_credit.html
Malvertizing just got a whole lot smarter.
With a stroke of genius, a new approach allows hackers to determine if you are running IE without up to date antivirus and then using several flash vulnerabilities, attack your pc using steganography.
It’s like a ninja sneaking up on you, deadly, virtually undetectable and very smart.
Thinking of using your debit card at the pump, think again
Visa Delays Chip Deadline for Pumps To 2020 https://krebsonsecurity.com/2016/12/visa-delays-chip-deadline-for-pumps-to-2020/
Caving to the Convenience store lobby, Visa has delayed making the move to chip and pin which can make your debit cards huge win in a skimmer. If you are at a pump that does not use a chip reader, DO NOT USE YOUR DEBIT CARD!
Newly discovered router flaw being hammered by in-the-wild attacks | Ars Technica
It seems painfully clear to most security researchers now that the Mirai botnet is not finished and may never be unless providers take security seriously.
In an article from Arstechnica,
They explain that the loophole being exploited now deals with remote management ports for devices that our cable and DSL providers use. With most of the home users struggling to setup these devices when they get them home, they seldom change the default passwords and that allows hackers to exploit them. Vendors are also leaving application ports open to the Internet without proper source filtering which allows them to be enumerated by tools like Shodan and Censys.
We simply need to get better at taking ownership of our security posture, both consumers and vendors alike. Let’s all step up out game…
SafetyNet: Google’s tamper detection for Android · John Kozyrakis ~ blog
Interesting article about Google’s idea to test for rooted phones for developers who want to make sure that your phone is ‘safe’ to run their applications.
Stay tuned for more hacking…
I was reading this article about the sentencing of a 17 year old in the UK for a Web attack that happened in 2015. He says he won’t do it again but do we really want that?
http://www.infosecurity-magazine.com/news/talktalk-breach-17yearold-confesses/
It tells us that several websites were vulnerable to a SQL injection attack which leaked personally identifiable info (Pii).
Aren’t we punishing the wrong people here? I mean his motives were to show off his abilities and not to obtain and exploit the data. It also appears that the site already knew about the attack and was not able to do anything to mitigate?
I know that we would all like to live in a world where lost wallets are always returned to us with all the money inside but isn’t the company primarily responsible for continuing to neglect the security of the data?
Until we start legislative accountability for companies that hold service availability over security, we will continue to have breaches. To penalize individuals who help to find these flaws instead of congratulating them is like forgiving the dog and scolding the bone for just being there.
Cirque du Soleil – Ole
Had a great night out in Mexico watching the new Cirque du Soleil production called ‘Joya’. I saw golfer Greg Norman at the event and the only thing I could think of saying to him was ‘Happy 20Th Anniversary’ 😦
Bruce Schneier on the most recent attack vector, USB sticks
Think of it, you walk into a building, see a computer that (hopefully) is locked and you plug in a USB device and walk away. Just like James Bond, you look at your watch and a few minutes pass by. You unplug your device and head back to the Astin Martin…
Well okay this part is fictitious but the rest isn’t. Read more about the the technique in this article.
https://www.schneier.com/blog/archives/2016/11/hacking_passwor.html
Feeling better that you bought an IPhone?
New Threat Can Auto-Brick Apple Devices http://krebsonsecurity.com/2016/04/new-threat-can-auto-brick-apple-devices/
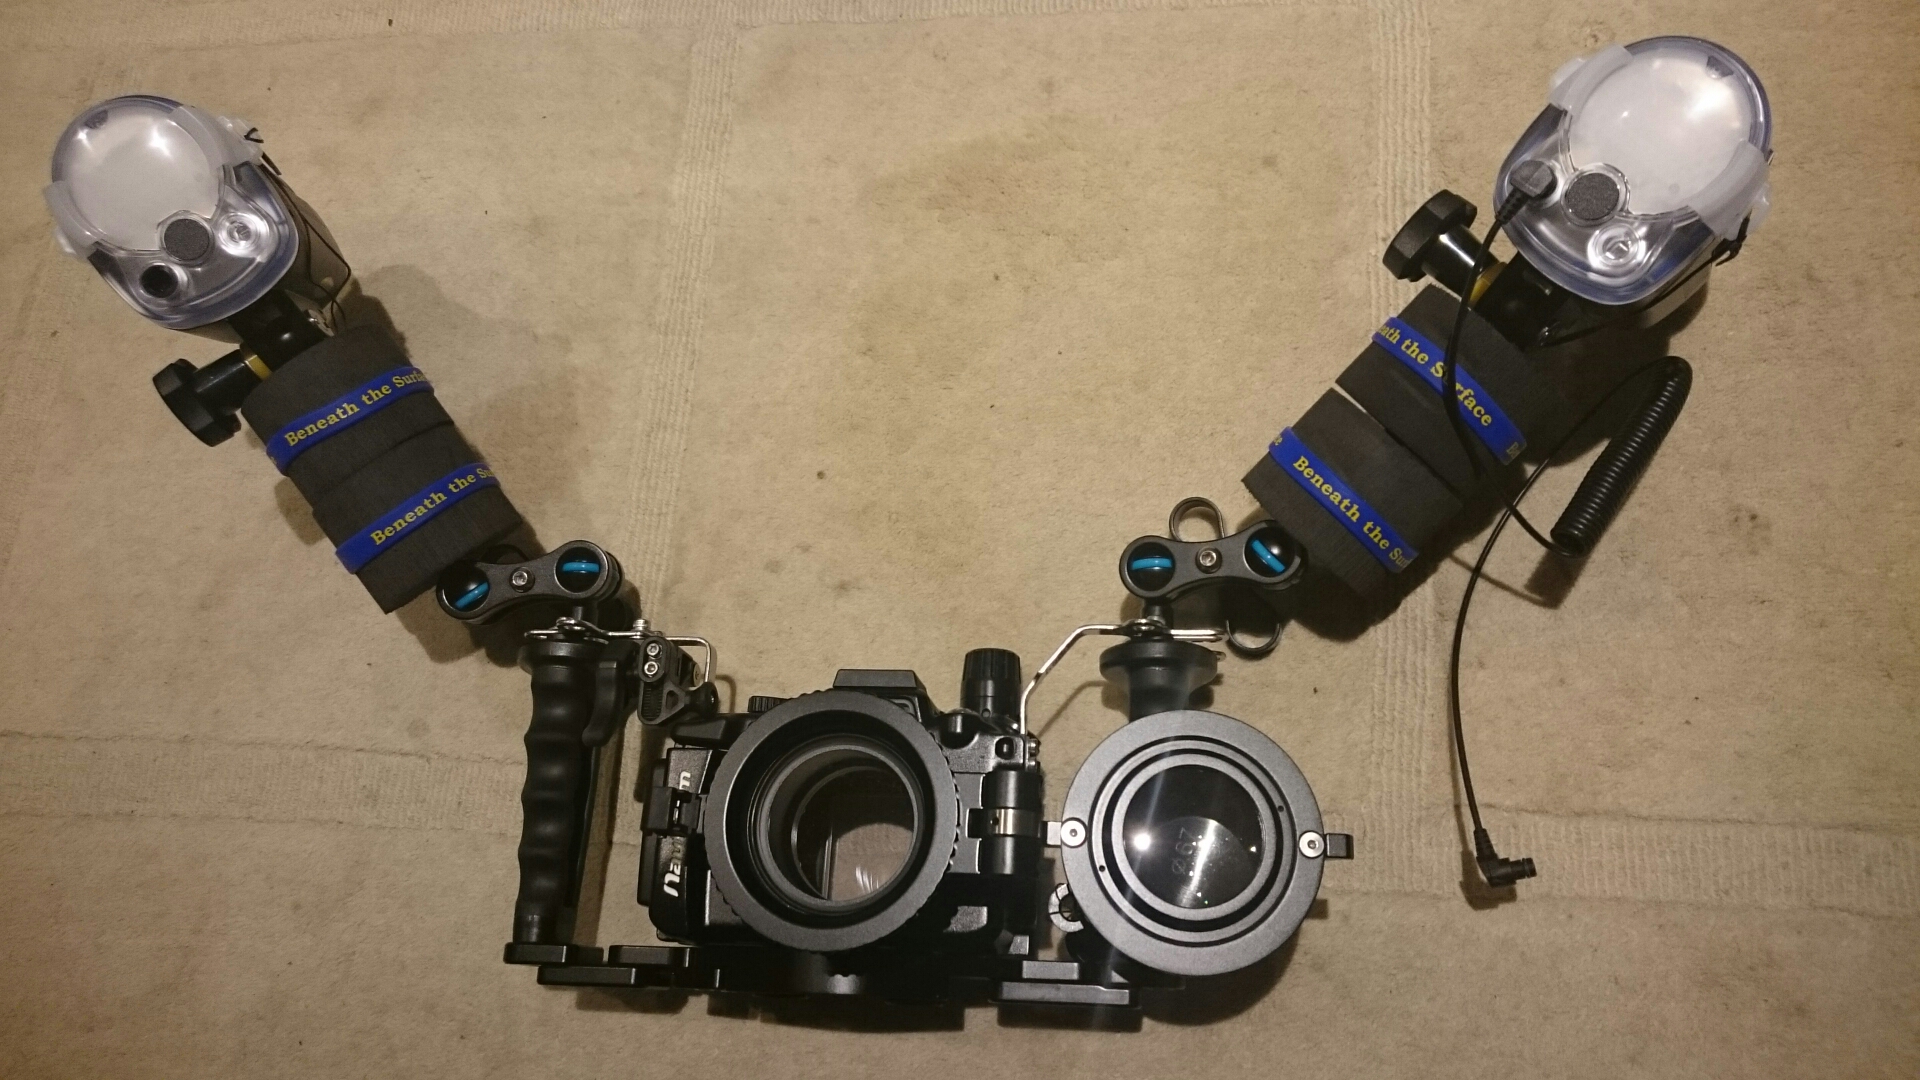
Getting ready to take more underwater pictures
I got another strobe and a new macro lens for our underwater rig today. Can’t wait to take some great pictures in Florida. Check out the flip mount for our diopter…